A couple of years ago I wrote a tweet thread about how I'd begun to see people in the crypto and finreg spaces expressing excitement about the traceability of cryptocurrencies.
Thinking back to it as I watch Senators and crypto industry executives talk about how delightfully traceable public blockchains are. No pesky warrant required!
A Coinbase data breach filing with the Maine Attorney General finally gives us some more detail than Coinbase’s vague “less than 1% of monthly transacting users”. 69,461 people were affected, and Coinbase says the data breach occurred on December 26, 2024.
It took them almost five months between the incident and the incident disclosure, although the company has since admitted it knew customer support agents were suspiciously accessing customer data as far back as January.
Security researchers who have spent months trying to call Coinbase’s attention to serious issues at the company are disputing Coinbase’s claims about the timing of the breach. “Threat actors had ongoing access via multiple insiders over a prolonged period of time.”
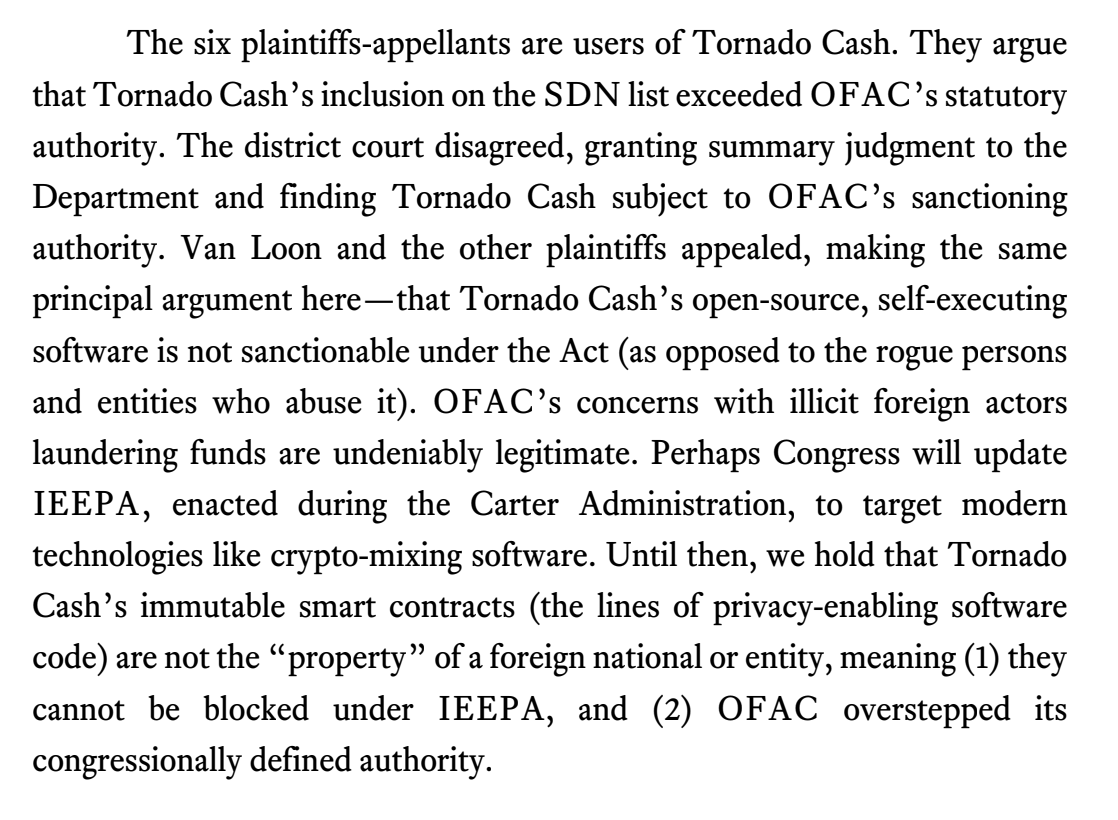
It's interesting to me that the Fifth Circuit only considered "control" at the smart contract level, and does not seem to consider the role of validators in their opinion. A substantial portion of ETH blocks are built with relays that censor transactions with OFAC-sanctioned contracts, and it seems to me there is now an open question as to whether validators that use non-censoring relays could be sanctioned directly.
(Not saying they should, just remarking on the fact that it seems to have gone completely unaddressed.)
Of course this was a concern already, but what with the Treasury focused on the Tornado Cash contracts, it was less central than I suspect it might be soon. This strategy would be somewhat in keeping with legal theories around other "malicious" code, where it's broadly speaking legal to write a devastating computer virus, but a whole lot less legal to run one.
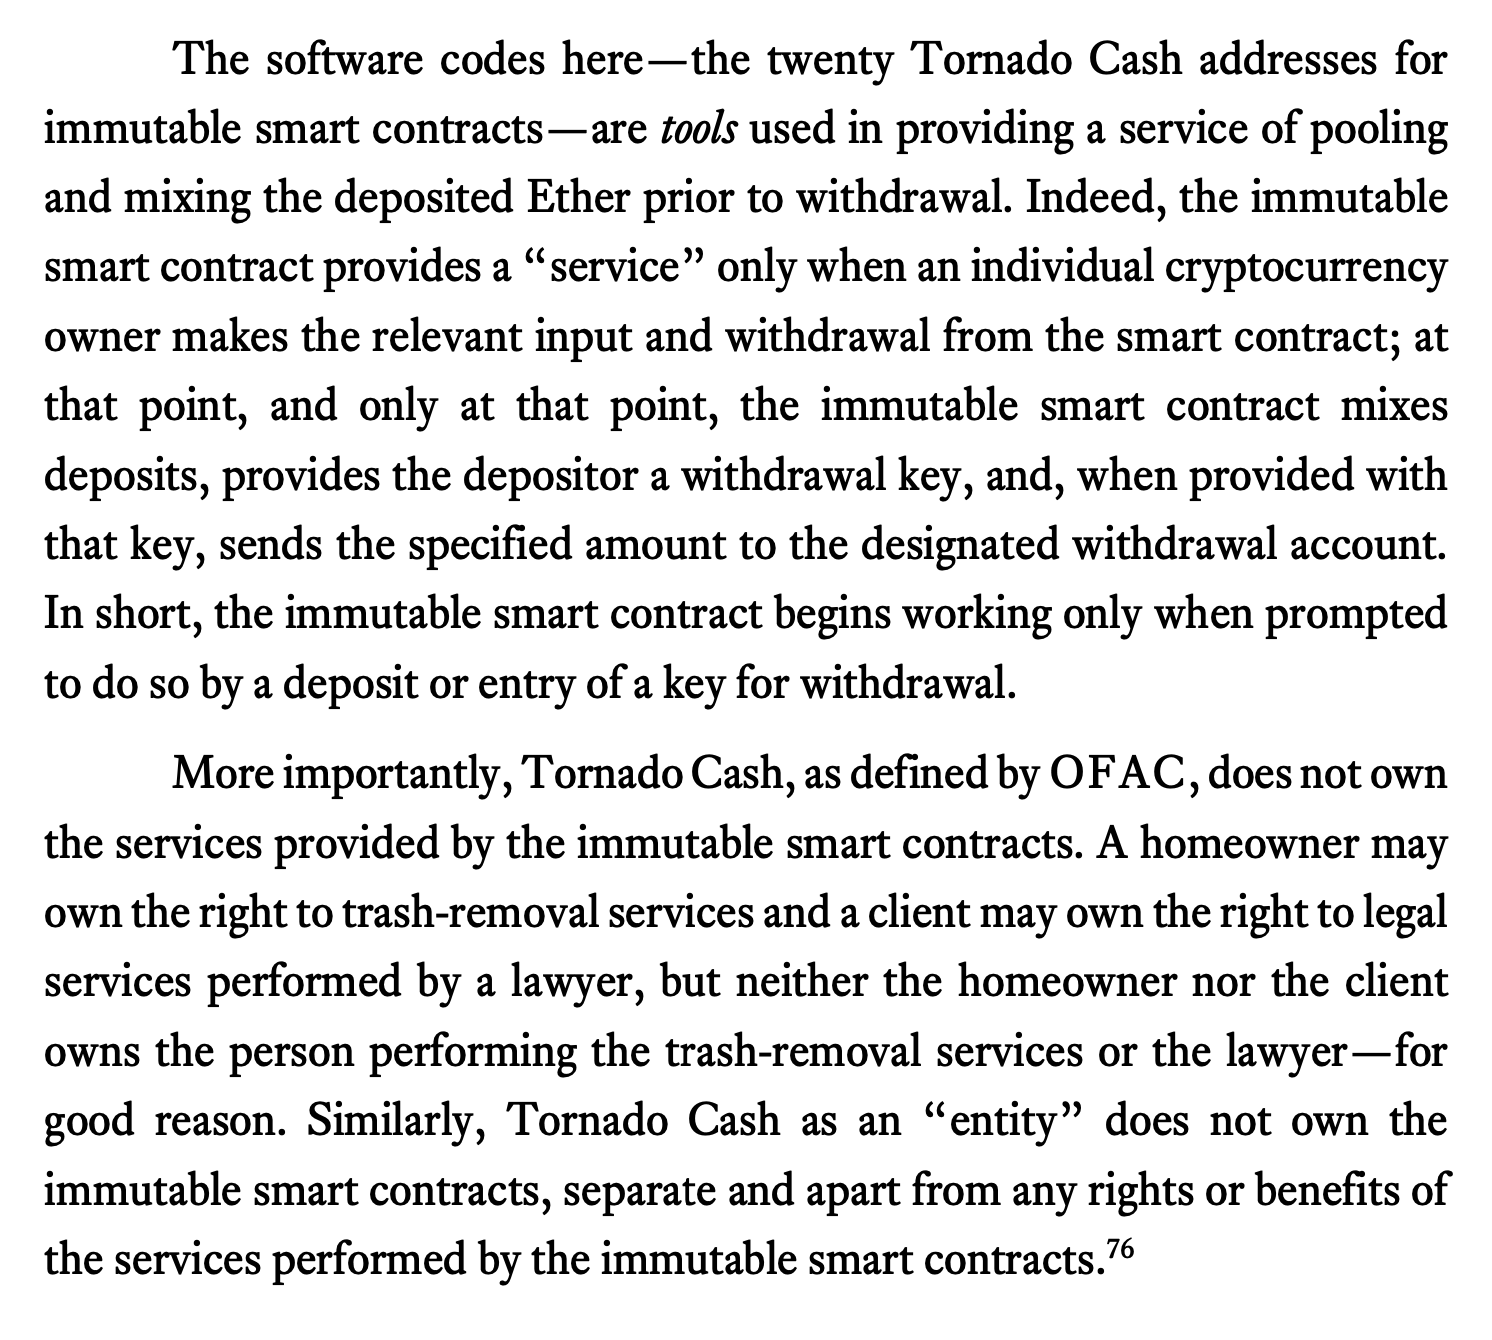
The Fifth Circuit has just opined that the smart contracts that comprise the Tornado Cash cryptocurrency tumbler are "not property because they are not capable of being owned", and thus cannot be sanctioned by OFAC.
I must once again urge you: please do not record your abortions on the blockchain.
There are a lot of very worried people right now, fearful of an impending regime that may well crack down on things like reproductive care, gender-affirming care, or the ability for immigrants to even continue to remain in the US. Some have suggested people get familiar with cryptocurrencies in the event they might have to circumvent an authoritarian state.
I’ve said it before and I’ll say it again: in very bad situations, bad solutions can sometimes still be better than nothing. I make no secret of my views on the cryptocurrency industry, but I am the last to judge a person for using whatever means they have available to them to take care of themselves and others.
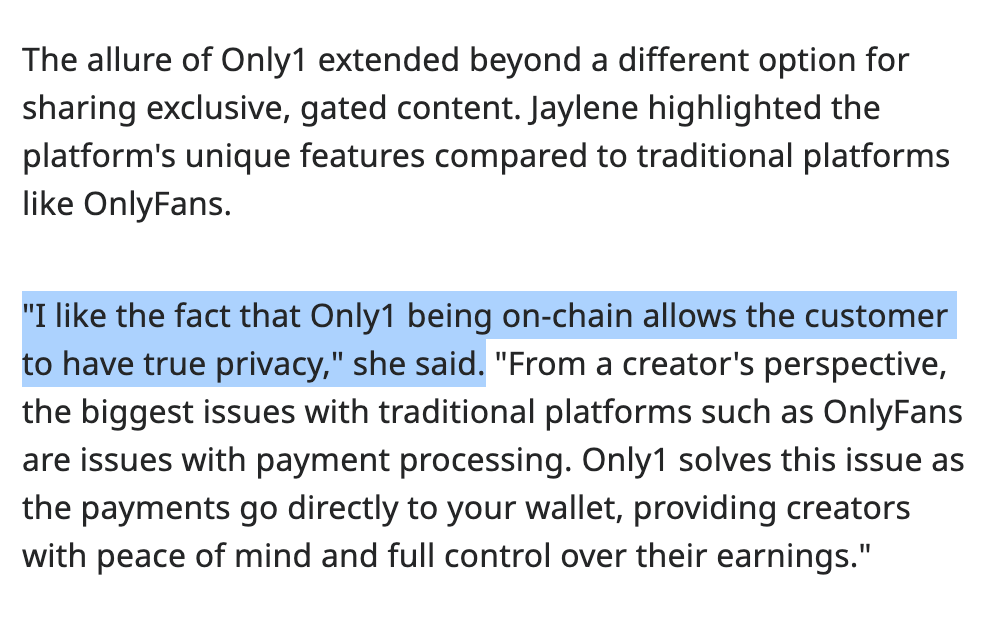
PSA: Paying for a subscription on the crypto version of OnlyFans using a public blockchain does not give you "true privacy", regardless of what the models there might say.
There’s people who are really angry about a lot of tech stuff who disagree with each other about everything, including whether or not they really even have a problem. But all of their problems start with the fact that there’s a lot of commercial surveillance. So these people might disagree about everything else, but they will agree that their problem could be solved if we could do something about commercial surveillance.
So if you think Mark Zuckerberg made grampy into a QAnon, or if you think Insta made your teenager anorexic, or if you think that TikTok is convincing millennials to quote Osama bin Laden, right? Or if you think that it’s ugly that red state attorneys general are following teenagers into out-of-state abortion clinics, or that Google reverse warrants reveal the identity of everyone in a black lives matter demonstration or for that matter, the January 6th riots, or if you are worried about deep fake porn, or if you’re worried that people of color are having the surveillance data captured about them mobilized to discriminate against them in employment and financial products, right? All of these different things all start with cutting off the supply of surveillance data.
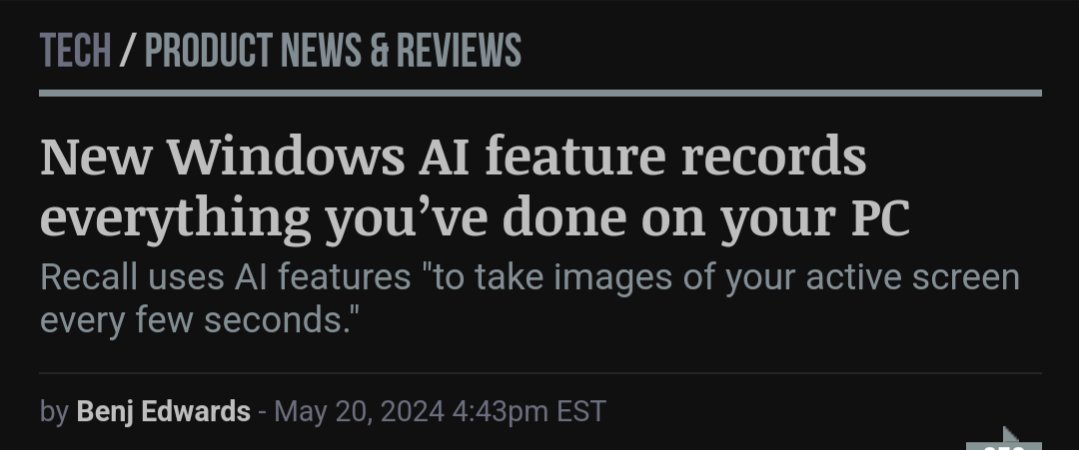
"it's all stored locally" is not a panacea for these alarming privacy-invading products!
what exactly is stored locally? what data is extracted from that local data and sent to the company's servers? is that local data being backed somewhere?
what additional risks are now being posed to people who share devices, whose devices might be accessed by others or compromised, or who might not realize these tools are running? what is the risk that the company might later change its decision on local storage?